RECOVERIS TURNS ONE · PORTO
Recoveris had its first anniversary since founding, and we have great things coming.
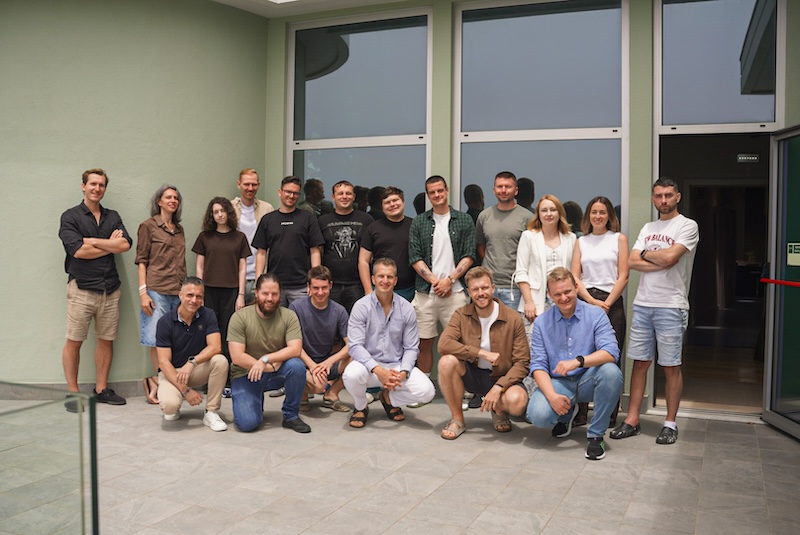
Recently, the whole team was in Porto for a week of strategy sessions, product workshops, and the kind of team building that only happens in person. It capped a first year in which we drove a $10.5M freeze behind one of the largest crypto seizures in Swiss history, ran the investigation that broke the ZondaCrypto story before regulators acted, took on mandates with players like UPbit, Sygnum, and EY, and trained investigators with Interpol, Europol, and the OSCE across 11 countries.
The shift we most want to mark is going from investigation-led and AI-assisted to technology-led and expert-backed, with the technology at the core and our experts in command. Every case we run and every investigator decision feeds our products and our proprietary AI model, so the cases we solve today train the system that will run them tomorrow.
June in on-chain investigations.
Once a month we summarise the patterns from recent incidents, explain one concept in plain language for legal and compliance professionals, share what we’re shipping, and tell you how to reach us when you need an expert source.
Less than 5 minutes to read · Forward freely
Last weeks · May 18 – June 28
The patterns we saw.
Our weekly deep-dives covered the period’s most instructive exploits, more than $46M drained across the cases we looked at, set against the $344M Tether seizure, one of the largest of the year. Four threads ran through them.
1 · Key handling
The contracts worked as written, but the keys didn’t.
Humanity Protocol lost about $36M because a multisig that looked safe on-chain had several of its keys sitting on a single laptop. Nothing in the code failed. Three of 2026’s four largest exploits have come down to how keys were handled rather than a bug in the contract.
2 · Attack surface
Attackers are moving off the contract entirely.
The entry points this period sat around the code rather than inside it. The Verus exploit came through a cross-chain bridge, Polymarket’s losses came from a compromised vendor that injected JavaScript into its own site, and the jaredfromsubway drain turned a trading bot’s approval logic against it.
3 · Preparation
The groundwork is often the best evidence.
Several of these attacks were set up weeks ahead, with wallets pre-funded and contracts deployed long before the theft. That preparation is permanent and timestamped on-chain, and it tends to be the richest part of the case file, because it reads as premeditation rather than opportunism.
4 · Enforcement
Seizures are getting bigger and faster.
Against those losses, the Tether case saw about $344M seized, part of roughly $9B frozen in a single week of coordinated action. The machinery for cross-border freezes is maturing, and a well-documented freeze request is now realistic in the first days of a case rather than months later.
Source: CoinDesk on the $344M Tether freeze →
Full weekly breakdowns and sources: recoveris.io/blog →
CONCEPT OF THE MONTH
Token approvals and multisig, explained.
Plain language for legal and compliance professionals
Two of this period’s biggest losses came down to mechanics worth understanding, because the same mechanics turn up in the cases that reach a lawyer’s desk. The first is the token approval. When someone uses most tokens in DeFi, they don’t hand the tokens over directly. They sign an approval that grants a smart contract permission to move the tokens on their behalf. That permission is convenient, and it’s also the most common way wallets get drained: a malicious or compromised contract with a standing approval can pull the funds whenever it chooses. June’s jaredfromsubway case ran on exactly this: an automated trading bot was baited into granting approvals to attacker-controlled contracts, which then drained roughly $7.5M in a single sweeping transaction. There was no phishing link and no stolen key, only standing approvals that were never closed. A client who signs a malicious permit on a phishing site loses funds the same way: a different entry point, the same mechanism.
The second is the multisig. A multisig wallet is meant to require several people to sign off before money moves, say three approvals out of six keyholders, so that no single person, and no single stolen key, can move the funds alone. It only delivers that protection if the keys are genuinely held by different people on different devices. Humanity Protocol lost about $36M because several of its keys had been backed up to one laptop. When that laptop was compromised, a three-of-six wallet quietly became a one-of-one. The contract did exactly what it was written to do. The key handling is where it failed.
A multisig protects you only when the keys are truly separated. An approval grants the power to take the funds; the loss itself lands later, when that power is exercised, and both steps are timestamped to the block.
For anyone building a case, both shift where the decisive evidence sits. With an approval, two on-chain events frame the loss: the approval that grants permission, and the later transfer that actually drains the funds. The transfer is the decisive timestamp and the start of the traceable path into liquid assets, and where the victim signed an off-chain permit rather than an on-chain approval, that signature leaves no block timestamp until the attacker submits it. With a multisig, the on-chain admin steps are timestamped too, but the real story often sits off-chain, in how the keys were stored and who had access. Both reward speed, because a documented freeze request has a real chance only while the funds stay put.
Further reading
Token approvals explained · Ledger Academy
Check and revoke wallet approvals · Revoke.cash
What a multisig wallet is · Ledger Academy
Safe, the standard multisig · safe.global
FROM RECOVERIS
What we’ve been working on.
Partnership

EY DLA went live, June 2 in Zurich.
Our joint offering with EY, Distributed Ledger Analysis (DLA), launched at EY’s Crypto Compliance Breakfast in Zurich. It brings source-of-funds tracing, custody verification, and AML risk scoring to banks and family offices at the institutional level, the workflow their compliance teams are most likely to meet next.
Law enforcement training
Training the investigators who work these cases.
Our investigators spent much of the month in front of law enforcement. Alessandro Rella ran two OSINT courses for Italian agencies, including a full day of Bitcoin and crypto forensics on Anubitux, the open-source environment he and Umberto Buonora built so officers have a safe place to do cryptocurrency investigations. Umberto was in Rome for CEPOL’s International Asset Recovery course, hosted by the Guardia di Finanza, covering the part that breaks the traditional playbook: how value moves through mixers, bridges, and exchanges, and how on-chain findings turn into something that holds up for a freeze or a confiscation order.
Public-private networks
Sol Cinosi at the IVAN Summit.
As a member of IVAN, the Illicit Virtual Asset Notification network that links law enforcement and private forensic firms to share illicit-address intelligence close to real time, Recoveris had our Chief Government and Corporate Affairs Officer, Sol Cinosi, on stage at the IVAN Summit at MITRE in Virginia. Sol presented a case study from the ZondaCrypto investigation, showing how on-chain intelligence holds up across complex cross-border cases and feeds directly into recovery. The point the summit kept returning to is the one we see in our own casework: no single organisation traces, freezes, and recovers across borders on its own, and trusted information sharing matters as much as better technology.
Case insight
A romance scam the police first advised dropping.
At Asset Recovery CEE in Warsaw, Dawid Koperski walked through a case where a Swiss victim lost about $450K in ETH and USDT, and the police initially advised dropping it. Blockchain tracing, a forensic report, and coordination with exchanges and prosecutors across two jurisdictions produced a Swiss seizure order recovering over $72K, with around $60K more frozen in Thailand pending mutual legal assistance. The documentation had to hold up in two legal systems at once, which is the norm, not the exception, in cross-border recovery.
Webinar series · Digital Asset Recovery Around the World
Two recent sessions, on demand.
Ukraine: recovery under wartime controls
Fred Buret sat down with Dmytro Marchukov of Impacta Law. Ukraine runs most fraud matters through the criminal system and the cyber police, which opens tools civil claims can’t reach but hands control to overloaded authorities. With no licensed local exchanges, investigators build relationships with global ones directly, and the volatility of stolen crypto keeps reshaping the number you’re fighting for, with no guidance on which moment fixes its value.
USA: the most developed toolkit, and the most cross-border
Fred Buret with Daniel Coyle of Sequor Law. US courts now allow alternative service on anonymous defendants, including by NFT and on the blockchain itself, and TROs and prejudgment garnishment can freeze crypto while a case runs, as long as the funds sit with an exchange that holds KYC records and honours court orders. Jurisdiction still breaks down when assets follow an owner’s domicile across borders.
PRODUCT SPOTLIGHT
AURA: one defensible wallet-risk score.
Multi-provider wallet risk screening
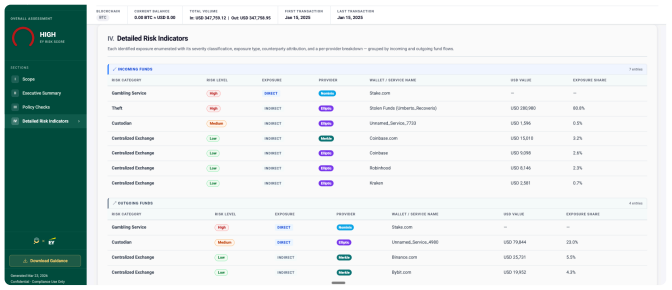
AURA is our multi-provider wallet risk screening product, and it fixes a problem any compliance team will recognise. No single analytics tool covers every case, two providers often disagree on the same address with no way to reconcile them, and a bare risk number never explains what’s driving it. AURA takes the data on one address from multiple providers, like Elliptic, Merkle Science, and Nominis, maps their different taxonomies into one model, and resolves the conflicts so no provider’s intelligence is lost.
The output is a single, defensible score you can drill into, with every agreement and disagreement surfaced on the page rather than hidden in a black box, structured as a regulator-ready report. It’s vendor-neutral, FATF-aligned, SOC 2 assured, and validated by EY, who name Recoveris as a key technical service provider. It’s built for banks, VASPs, and compliance teams, available as an API or a dashboard.
Need an expert on the record?
Working a case that needs a forensic blockchain expert? For a court-admissible tracing report, an expert witness, or technical input on a live recovery matter, reach out to [email protected]. Our investigations team responds within one business day.
Journalists covering crypto crime, DeFi exploits, asset recovery, or sanctions exposure can reach our investigations and corporate affairs teams on the record at [email protected].